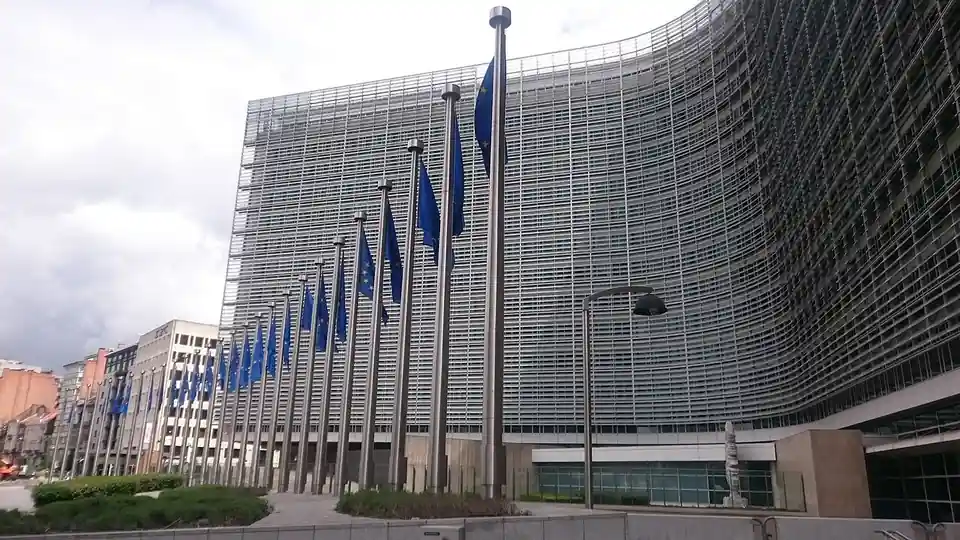
The European Commission has confirmed a network intrusion detected late last month. Officials identified that external threat actors targeted internal administrative systems on October 22 using an automated artificial intelligence platform. Following the European Commission AI cyberattack, technical staff disabled multiple applications to protect sensitive administrative networks. The incident prompted IT teams across the European Union to initiate rapid emergency defense measures.
Commission spokesperson Thomas Regnier confirmed the defensive actions during an official briefing. Regnier explained that administrators temporarily took down several applications as a protective and preventive step. The disruptions lasted for more than ten days, affecting planning tools, payroll processing, and the Commission’s Sysper human resources platform. Most of the affected systems have since been restored to normal operations, although certain programs, such as staff health insurance services, remained offline. Technical investigators found no evidence of a ransomware demand. Regnier also stated that investigators detected no evidence of a broader data breach affecting Commission staff as a whole. EU officials confirmed that the campaign utilized a publicly available AI tool, but declined to name the exact product.
For European civil servants, the prolonged system blackout caused practical disruptions to daily personnel administration, benefit claims, and internal communications. For external network administrators and business security teams, the incident shows how automated tools compress attack timelines. Malicious actors can now automate complex network reconnaissance without custom exploits. Security personnel must inspect exposed web services, enforce multi-factor authentication, and monitor privileged administrative accounts to protect against automated infiltration.
Autonomous Infiltration and the ARTEX Framework
While the Commission avoided naming the specific software, European cybersecurity agency CERT-EU issued a detailed warning on November 5. CERT-EU stated that recent automated intrusions against EU institutions highly likely involved ARTEX. ARTEX is an open-source penetration-testing platform driven by large language models. The software takes plain-language security instructions, breaks them into specific operational goals, and deploys autonomous AI agents to conduct reconnaissance and exploit testing. ARTEX does not contain an internal language model, but instead connects to external artificial intelligence providers. Following reports of real-world abuse, the original author took down the official repository in October 2026, though independent forks remain accessible.
Industry researchers corroborated the threat posed by this automated technology. On October 21, Microsoft Threat Intelligence reported that Storm-0940, a state-sponsored actor aligned with China, deployed ARTEX to target hundreds of organisations across multiple sectors. Microsoft confirmed that Storm-0940 used the framework during the ConnectWise supply chain intrusion. In several cases, attackers advanced from initial targeting to privileged cloud access in less than three hours. Investigators from Mandiant and Google Threat Intelligence Group verified Microsoft’s conclusions. Chris Dimitriadis, chief global strategy officer at ISACA, observed that artificial intelligence allows attackers to breach networks at the speed of intent.
Many cybersecurity professionals asked what AI tool was used in the European Commission cyber incident. Security agency CERT-EU assessed that the intrusion highly likely involved ARTEX. The utility links external language models to autonomous agents that execute security tasks. This mechanism enables external operators to probe target networks without crafting specialized attack code.
The October assault against the European Commission reveals how automated testing utilities can disrupt critical administrative networks. While core services such as Sysper have returned to operation, authorities continue to inspect perimeter defenses and cloud accounts. IT teams must remain vigilant against autonomous toolkits that accelerate infiltration. Technical evaluations continue behind closed doors, as the investigation is ongoing to establish whether sensitive records suffered any unauthorized access.